SOC 2 Type I vs Type II: Which One Do You Need
The difference between SOC 2 Type I and Type II, how the observation window works, what auditors test, what each costs, and how to decide which report your buyers accept.
Read articleComply more, complain less
Practical guidance on certification, security, privacy and AI governance, written by the consultants who deliver it. No jargon, no filler, just what the standards actually ask of you.
Latest

The difference between SOC 2 Type I and Type II, how the observation window works, what auditors test, what each costs, and how to decide which report your buyers accept.
Read article
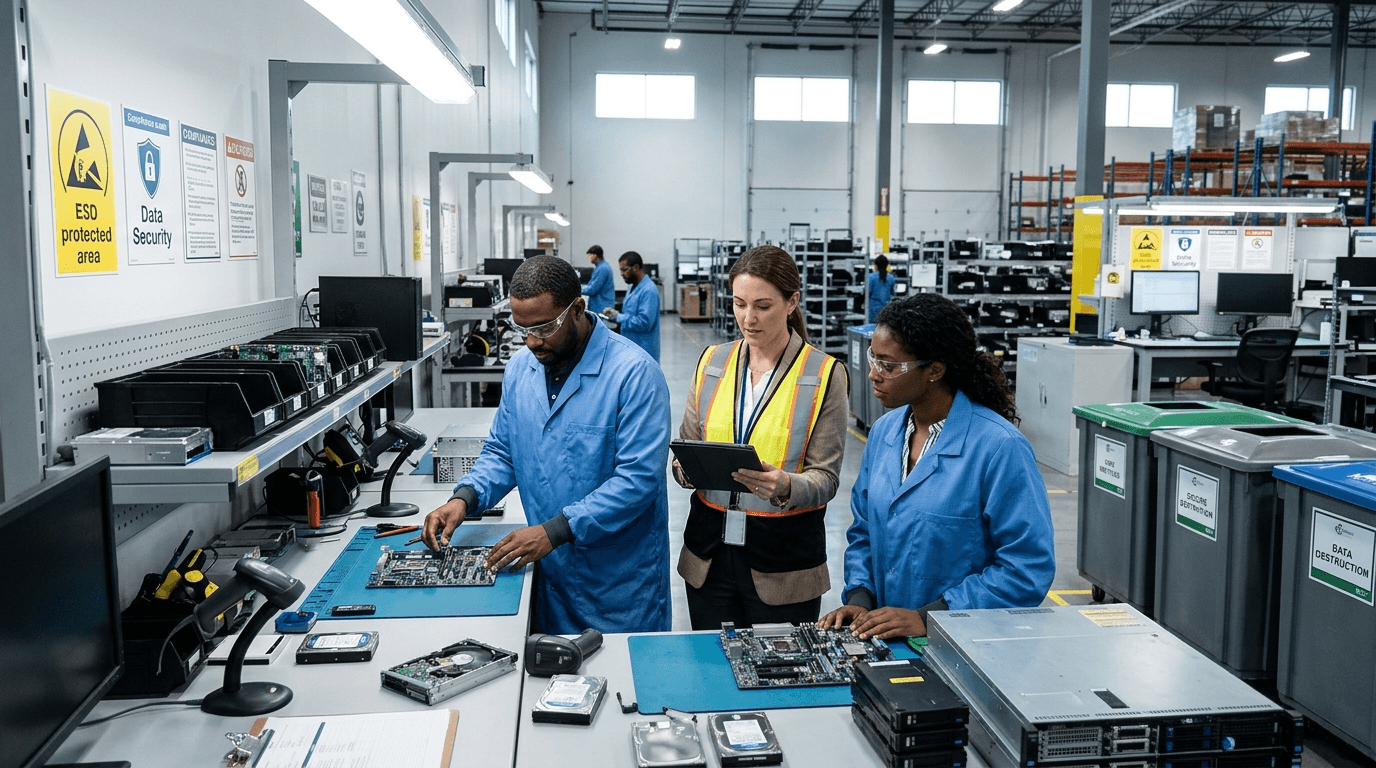
The ten R2v3 core requirements, the process appendices, how Core 7 and Appendix B differ, what auditors ask for, and what an Indian recycler needs before certification.
Read article
What SOC 2 involves for Indian SaaS selling to US buyers, Type I vs Type II, the Trust Services Criteria, realistic India cost and timeline, and how to get ready.
Read article
What the RBI cyber security framework requires of banks and NBFCs: IT governance, controls, VAPT, IS audit and incident reporting, and how to get inspection-ready.
Read article
A practical, step-by-step DPDP Act compliance checklist for Indian businesses: consent, notice, data principal rights, breach reporting and security safeguards.
Read article
India's DPDP Rules are live and AI governance is now a boardroom issue. See how ISO 42001 helps you meet DPDP obligations, cut audit effort, and win client trust.
Read articleContact us
Comply more, complain less
Tell us the certification or compliance goal in front of you, and we’ll show you the clearest path to reach it, and stay there.